Anyone working today knows: the boundaries between "private" and "business" blur — especially when business data is quickly uploaded to a personal Notion account, ChatGPT is asked for a nicer phrasing, or a presentation is saved in Google Drive "because it's more convenient."
The result: Shadow Data and Shadow AI — two phenomena as invisible as they are dangerous. And we observe them increasingly in Swiss companies.
This blog sheds light on what exactly lies behind them, where the risks are, why "ban" is not a solution, and how Meeting Metrics is working to offer a secure alternative.
What is Shadow Data?
Shadow Data refers to business data that ends up outside a company's official, controlled systems — mostly unintentionally, often for efficiency reasons.
Typical examples:
- Meeting notes are saved in private OneDrive accounts
- Customer information ends up in private ChatGPT accounts
- Documents are transferred to USB sticks
- Screenshots are shared in private WhatsApp groups
- Presentations are uploaded to tools that are not authorized
In short: data leaves the secure corporate environment and no one knows exactly where it goes or how it is processed.
Why does this happen?
The reasons are as human as they are pragmatic:
1) Employees want to work efficiently
If internal tools are too slow, limited, or complicated, people look for alternatives that seem faster, easier, and more modern.
2) AI tools are faster to access privately
GenAI tools like ChatGPT, Gemini, or Claude can be used privately within seconds — but often only after long IT approvals for business use.
3) Lack of internal alternatives
If modern tools are not officially provided, shadow solutions automatically arise.
4) "Just quickly..."
A classic phrase that has led to very long data problems in many companies.
Shadow AI: The new sibling of Shadow Data
With the spread of generative AI, a new term has emerged:
Shadow AI
This refers to the use of AI tools outside the official corporate ecosystem, often with sensitive data.
Swisscom clearly identifies Shadow AI as a risk:
"Shadow AI is a risk to a company's data security and compliance."
– Beni Eugster, Cloud Operation & Security Officer, Swisscom
According to the Microsoft Work Trend Index (2024), around 80% of GenAI users use tools via private accounts without approval, often unaware of the risk.
What makes this so dangerous?
- Business data ends up in AI tools whose storage location is unknown
- Data can be reused in training models
- Compliance (e.g., DSG / revDSG) can be violated
- IT departments have no transparency and no control
- Data can no longer be securely deleted
Many companies only realize in the event of an incident that data was processed somewhere it should never have been.
The risks of Shadow Data & Shadow AI
Here is a brief overview of the risks that particularly affect Swiss companies according to research, Swisscom Threat Radar & market analyses:
1) Loss of control
Employees do not know where the data goes.
IT knows even less.
2) Violation of data protection law (revDSG)
Sensitive data must not leave Switzerland without legal basis.
Many AI tools do exactly that — often unnoticed.
3) Data leaks & reputational damage
Especially with customer data, internal strategies, roadmaps, or personnel matters, data leaks can have serious consequences.
4) Use for model training
Many free AI tools retain user data or use it for training purposes.
5) Operational risks
- Multiple versions
- Faulty data
- Loss of knowledge
- No traceability
All this leads to inefficient processes and increases costs in the long term.
Why bans don't work
Swisscom puts it aptly:
"Employees want to use AI tools, whether the employer provides them or not."
Therefore, companies need controlled alternatives, not blacklists.
How Meeting Metrics creates a secure alternative
We observe daily that users copy meeting summaries or minutes into external GPTs to:
- Compose emails
- Write reports
- Analyze content
- Prepare follow-ups
- Gather information
That's understandable. It's fast. It's practical. But it's also risky.
That's why at Meeting Metrics we are developing a solution that addresses exactly this problem — without data leaving Switzerland.
The new Meeting Metrics chat feature: Secure AI in Switzerland
Our upcoming chat feature enables the following:
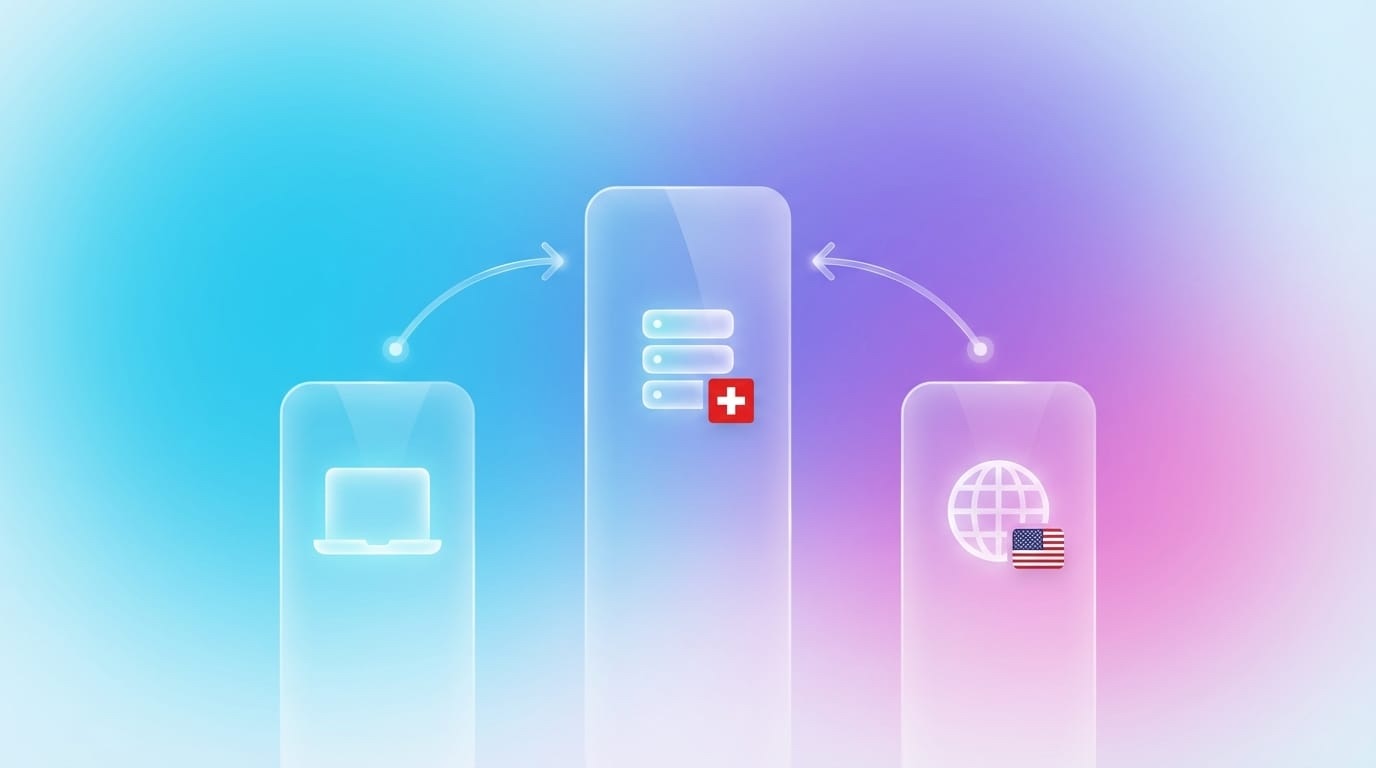
1) AI processing & storage in Switzerland
Data remains exclusively in Swiss data centers.
No export. No use for external training.
2) Questions about individual meetings
"What were the main decisions?"
"Give me a brief summary."
"Create an email to the customer based on that."
3) And new: Questions about entire folders
This is a real game changer.
Employees will be able to:
- Use entire folders with meeting summaries
- Minutes spanning several months
- Presentations & working documents
as a knowledge base.
Examples:
- "What were the most important risks from all Steering Committees in 2025?"
- "How has the project progress developed according to the last 10 meetings?"
- "Create an executive summary based on the last three months of customer feedback."
This transforms meeting content into a company-wide, secure, long-term knowledge source.
The opportunity: From Shadow Data → Secure AI Workspace
Shadow Data and Shadow AI arise because employees want to work efficiently.
Instead of preventing this, we build a solution that:
- Offers modern AI functions
- Guarantees Swiss data protection
- Secures data sovereignty
- Supports real workflows
A secure AI workspace without downsides.
Shadow Data and Shadow AI will not disappear. But how companies deal with them determines security, efficiency, and competitiveness.
With Meeting Metrics, we create an alternative that is more modern, safer, and more practical than any shadow solution. So that business meetings, minutes, and internal documents stay exactly where they belong: under control, in Switzerland, and intelligently usable at the same time.